
Certified AI Security Professional (CAISP) – AI Security Certification & Training
Build the practical skills required to identify, assess and reduce security risks across AI models, Large Language Models, RAG applications, AI agents, enterprise data and production AI systems. The Certified AI Security Professional (CAISP) program combines structured AI security training, hands-on exercises, realistic security scenarios, assessments and certification preparation to help professionals move from traditional cybersecurity concepts to the emerging discipline of securing AI systems.
- In-detailed Learning Materials
- Important IT Service Management Practices.
- Real World Application Via Case Studies
- Global Recognition For IT Services.

Certified AI Security Professional Course Overview
Artificial intelligence introduces a security layer that conventional application and infrastructure security alone does not fully address. AI systems can be exposed to prompt injection, malicious inputs, training-data manipulation, insecure model outputs, sensitive-data leakage, excessive agent permissions, vulnerable retrieval pipelines and attacks against models and the systems around them.
The Certified AI Security Professional (CAISP) certification is designed to develop practical knowledge for protecting modern AI applications across their lifecycle from architecture and data preparation to model deployment, runtime monitoring and incident response.
This AI security certification covers security considerations across machine learning systems, Generative AI, Large Language Models, Retrieval-Augmented Generation, vector databases and AI-powered applications. Participants learn how to identify attack surfaces, assess AI-specific threats, design security controls and support safer AI deployment in enterprise environments.
Unlike an introductory cybersecurity course that focuses primarily on conventional networks, endpoints and applications, the CAISP course concentrates on the security challenges created when models, prompts, embeddings, external knowledge, APIs, tools and autonomous agents become part of the application architecture.
The program is relevant to cybersecurity practitioners, AI/ML professionals, cloud and DevSecOps teams, security architects, risk professionals and engineers who need a structured approach to securing AI systems.
CAISP training also explores security across the complete AI lifecycle so that learners can understand not only how an AI attack occurs, but where controls should be introduced to prevent, detect and respond to it.
What You Will Get?
Learning Outcomes: AI Security Certification
After the completion of the course, the participants would be able to:
Training Calendar
English
- Self paced videos, assessments, recall quizzes, more
- For more details, reach us at training@novelvista.com
Includes Training, Exam & Certification
Lifetime Access
- Self paced videos, assessments, recall quizzes, more
- For more details, reach us at training@novelvista.com
Includes Training, Exam & Certification
CAISP Training Curriculum
The Certified AI Security Professional curriculum progresses from foundational AI security concepts into model, data, Generative AI, RAG and production-security practices.
Module 1: AI Security Foundations & Architecture+
Build the foundation required to understand the AI attack surface.
Key areas include:
- Introduction to AI security
- AI and machine-learning security fundamentals
- Components of modern AI systems
- AI application architectures
- AI assets and trust boundaries
- AI attack surfaces
- Shared responsibility for AI security
- Security across the AI lifecycle
- Secure AI architecture principles
This module helps learners understand why AI security must consider the full system surrounding a model not only the model itself.
Module 2: AI Threat Modeling & Risk Assessment+
Learn how to systematically identify AI security threats before they become production incidents.
Topics include:
- AI threat modeling principles
- Asset identification
- Attack-surface mapping
- Trust-boundary analysis
- Threat actors
- Attack vectors
- Risk identification
- Likelihood and impact analysis
- Security control selection
- Residual risk
- AI security assessment workflows
Learners develop a repeatable process for evaluating AI architectures from an attacker and defender perspective.
Module 3: AI Data Security & Privacy+
AI systems depend heavily on data, making data protection a core component of AI security.
Topics include:
- AI data lifecycle
- Training-data security
- Data provenance
- Data integrity
- Sensitive-data classification
- Data leakage risks
- Privacy considerations
- Unauthorized data exposure
- Data-access controls
- Secure data pipelines
- Poisoning risks
- Data monitoring and auditability
This module focuses on protecting information before, during and after it interacts with AI systems.
Module 4: Model Security & Adversarial Machine Learning+
Understand how attackers can target machine-learning models and how security teams can assess those risks.
Topics include:
- Introduction to adversarial machine learning
- Model attack surfaces
- Data poisoning
- Adversarial inputs
- Evasion attacks
- Model manipulation
- Model extraction concepts
- Information leakage
- Model integrity
- Adversarial testing
- Detection strategies
- Defensive controls
- Model monitoring
Learners build an understanding of how AI models may behave differently under adversarial conditions and why security testing must account for those scenarios.
Module 5: Generative AI, LLM & Prompt Security+
Large Language Models introduce security risks that go beyond conventional application input validation.
Topics include:
- LLM application architecture
- Prompt security
- Direct prompt injection
- Indirect prompt injection
- Jailbreak attacks
- Sensitive information disclosure
- Insecure model outputs
- Excessive trust in generated responses
- Input validation
- Output filtering
- Guardrails
- System-prompt protection
- Tool-use risks
- LLM API security
- Security testing for Generative AI applications
This module helps participants develop practical security thinking around applications built with modern LLMs.
Module 6: RAG, Vector & Knowledge Security+
Retrieval-Augmented Generation connects AI models to enterprise knowledge, creating powerful capabilities and new security boundaries.
Topics include:
- RAG security architecture
- Retrieval attack surface
- Vector database security
- Embedding-related considerations
- Knowledge-base access control
- Document-level authorization
- Retrieval permissions
- Metadata security
- Knowledge poisoning
- Malicious retrieved content
- Indirect prompt injection through documents
- Sensitive-information retrieval
- Input and output controls
- Retrieval logging
- Secure indexing
The goal is to prevent an AI assistant from becoming an unintended route around enterprise information-access controls.
Module 7: AI Runtime Security, Monitoring & Incident Response+
AI security does not end when a system reaches production.
This module focuses on continuous protection.
Topics include:
- Production AI security
- Runtime monitoring
- AI security telemetry
- Logging
- Suspicious prompt patterns
- Abnormal model behavior
- Access monitoring
- Security alerts
- AI incident identification
- Incident triage
- Containment
- Investigation
- Recovery
- Post-incident analysis
- Continuous improvement
Learners explore how existing security operations can evolve to monitor AI-specific behavior and attack patterns.
Module 8: AI Security Governance, Standards & Assurance+
Technical security controls must connect with organizational risk management and governance.
Topics include:
- AI security governance
- Security roles and responsibilities
- AI security policies
- Control ownership
- Security assurance
- Risk acceptance
- Security reviews
- AI security documentation
- Continuous assurance
- Relevant AI security frameworks and industry guidance
- Secure AI lifecycle practices
- Governance integration
This module helps learners connect engineering controls with broader enterprise security and assurance responsibilities.
Course Details
Get a comprehensive overview of what to expect in our Certified AI Security Professional (CAISP) Course through this detailed breakdown. Designed to build practical expertise in securing modern AI systems, this section covers the key elements of the CAISP Certification, including prerequisites, key benefits, skills covered, and training delivery style.
Whether you're entering the field of AI security or strengthening your existing cybersecurity expertise, the Certified AI Security Professional Course helps you develop practical knowledge in AI threat modeling, LLM security, prompt injection defense, RAG security, AI agent security, adversarial machine learning, and secure AI architecture. Our CAISP Course is structured to support professionals preparing for emerging AI security roles and organizations looking to strengthen their AI security capabilities across the USA, India, Canada, the UK, UAE, Saudi Arabia, Australia, Germany, and worldwide.
Who Should Take the CAISP Certification?+
The CAISP course is designed for professionals involved in building, deploying, protecting, auditing or governing AI systems.
Suitable roles include:
- Cybersecurity Professionals
- Security Analysts
- Security Engineers
- Security Architects
- Application Security Professionals
- Cloud Security Engineers
- DevSecOps Engineers
- AI Engineers
- Machine Learning Engineers
- Data Scientists
- AI/ML Architects
- Solution Architects
- Cloud Architects
- SOC Professionals
- Threat Analysts
- Penetration Testers
- Red Team Professionals
- Information Security Managers
- AI Governance Professionals
- Technology Risk Professionals
- Privacy and Compliance Professionals
- Technical Consultants
- Professionals working toward an AI Security Engineer role
The program can also benefit engineering leaders responsible for approving AI systems for production.
CAISP Eligibility+
CAISP is particularly relevant for professionals with exposure to one or more of the following areas:
- Cybersecurity
- Information security
- Application security
- Cloud security
- DevSecOps
- Software engineering
- AI engineering
- Machine learning
- Data science
- Enterprise architecture
- Technology risk
- AI governance
Professionals do not necessarily need to work as an AI security engineer before studying AI security.
However, some understanding of technology, security or AI concepts will make advanced technical material easier to absorb.
CAISP Prerequisites+
Recommended background before taking CAISP training includes:
- Basic cybersecurity concepts
- Familiarity with authentication and access control
- Basic understanding of APIs and modern applications
- General awareness of cloud or application architecture
- Introductory understanding of AI and machine learning
- Awareness of Large Language Models and Generative AI
Prior professional AI-security experience is not required for learning the material unless NovelVista establishes a formal certification prerequisite.
Skills Covered in AI Security Training+
CAISP training develops knowledge across several interconnected AI security domains.
AI Threat Modeling
Identify assets, attackers, entry points, trust boundaries and potential abuse scenarios across an AI system.
Adversarial Machine Learning
Understand attacks that target model behavior, data integrity, confidentiality and availability.
AI Data Protection
Protect training, inference, retrieval and enterprise data from unauthorized exposure and manipulation.
LLM Security
Assess security risks associated with prompts, context, generated responses and external integrations.
Prompt Injection Defense
Understand direct and indirect prompt attacks and design layered safeguards rather than relying on prompts alone.
RAG Security
Protect retrieval systems, vector databases and enterprise knowledge from unauthorized access or manipulation.
AI Agent Security
Apply identity, authorization, least privilege and tool-access controls to AI agents that can perform actions.
AI Security Testing
Evaluate how AI systems behave under intentionally malicious or abnormal inputs.
AI Monitoring
Identify security signals, logging requirements and abnormal behaviors associated with production AI.
AI Incident Response
Prepare teams to investigate, contain and learn from AI-related security incidents.
AI Security Governance
Connect technical safeguards with policy, risk ownership, control assurance and continuous monitoring.
Key Benefits of CAISP Training+
Develop AI-Specific Security Expertise
Traditional cybersecurity knowledge remains valuable, but AI introduces additional attack surfaces.
CAISP helps practitioners extend existing security thinking to models, prompts, data, RAG systems and agents.
Learn to Secure Modern AI Applications
Develop practical security knowledge relevant to:
- LLM applications
- Enterprise copilots
- RAG applications
- AI agents
- Machine-learning models
- AI APIs
- AI-enabled business workflows
Build Hands-On Security Capability
The course emphasizes application through labs, exercises, threat models and realistic security scenarios.
Bridge AI Engineering and Cybersecurity
AI security often sits between engineering and security teams.
The course helps professionals understand both sides of that boundary so they can communicate more effectively about technical AI risk.
Prepare for Emerging AI Security Responsibilities
Organizations adopting AI increasingly need professionals who can evaluate AI architectures, identify AI-specific risk and help establish security controls.
CAISP provides a structured learning path for developing that capability.
Is CAISP the Right AI Security Course for You?+
CAISP may be a strong fit if:
- You already work in cybersecurity and want to specialize in AI.
- You are an AI engineer who wants stronger security skills.
- You build LLM, RAG or AI-agent applications.
- You perform security architecture or application-security reviews.
- You need to assess AI systems before production deployment.
- You work in cloud security or DevSecOps.
- You are responsible for AI risk or security governance.
- You want to work toward an AI security engineer role.
- You prefer practical security work over theory-only learning.
CAISP may not be the right choice if your goal is only to learn general cybersecurity fundamentals or if you are looking exclusively for non-technical AI governance training.
Professionals focused primarily on policy, compliance, accountability and responsible-AI operating models may also want to explore an AI Governance Certification alongside technical AI security training.
AI Security Certification Exam Details
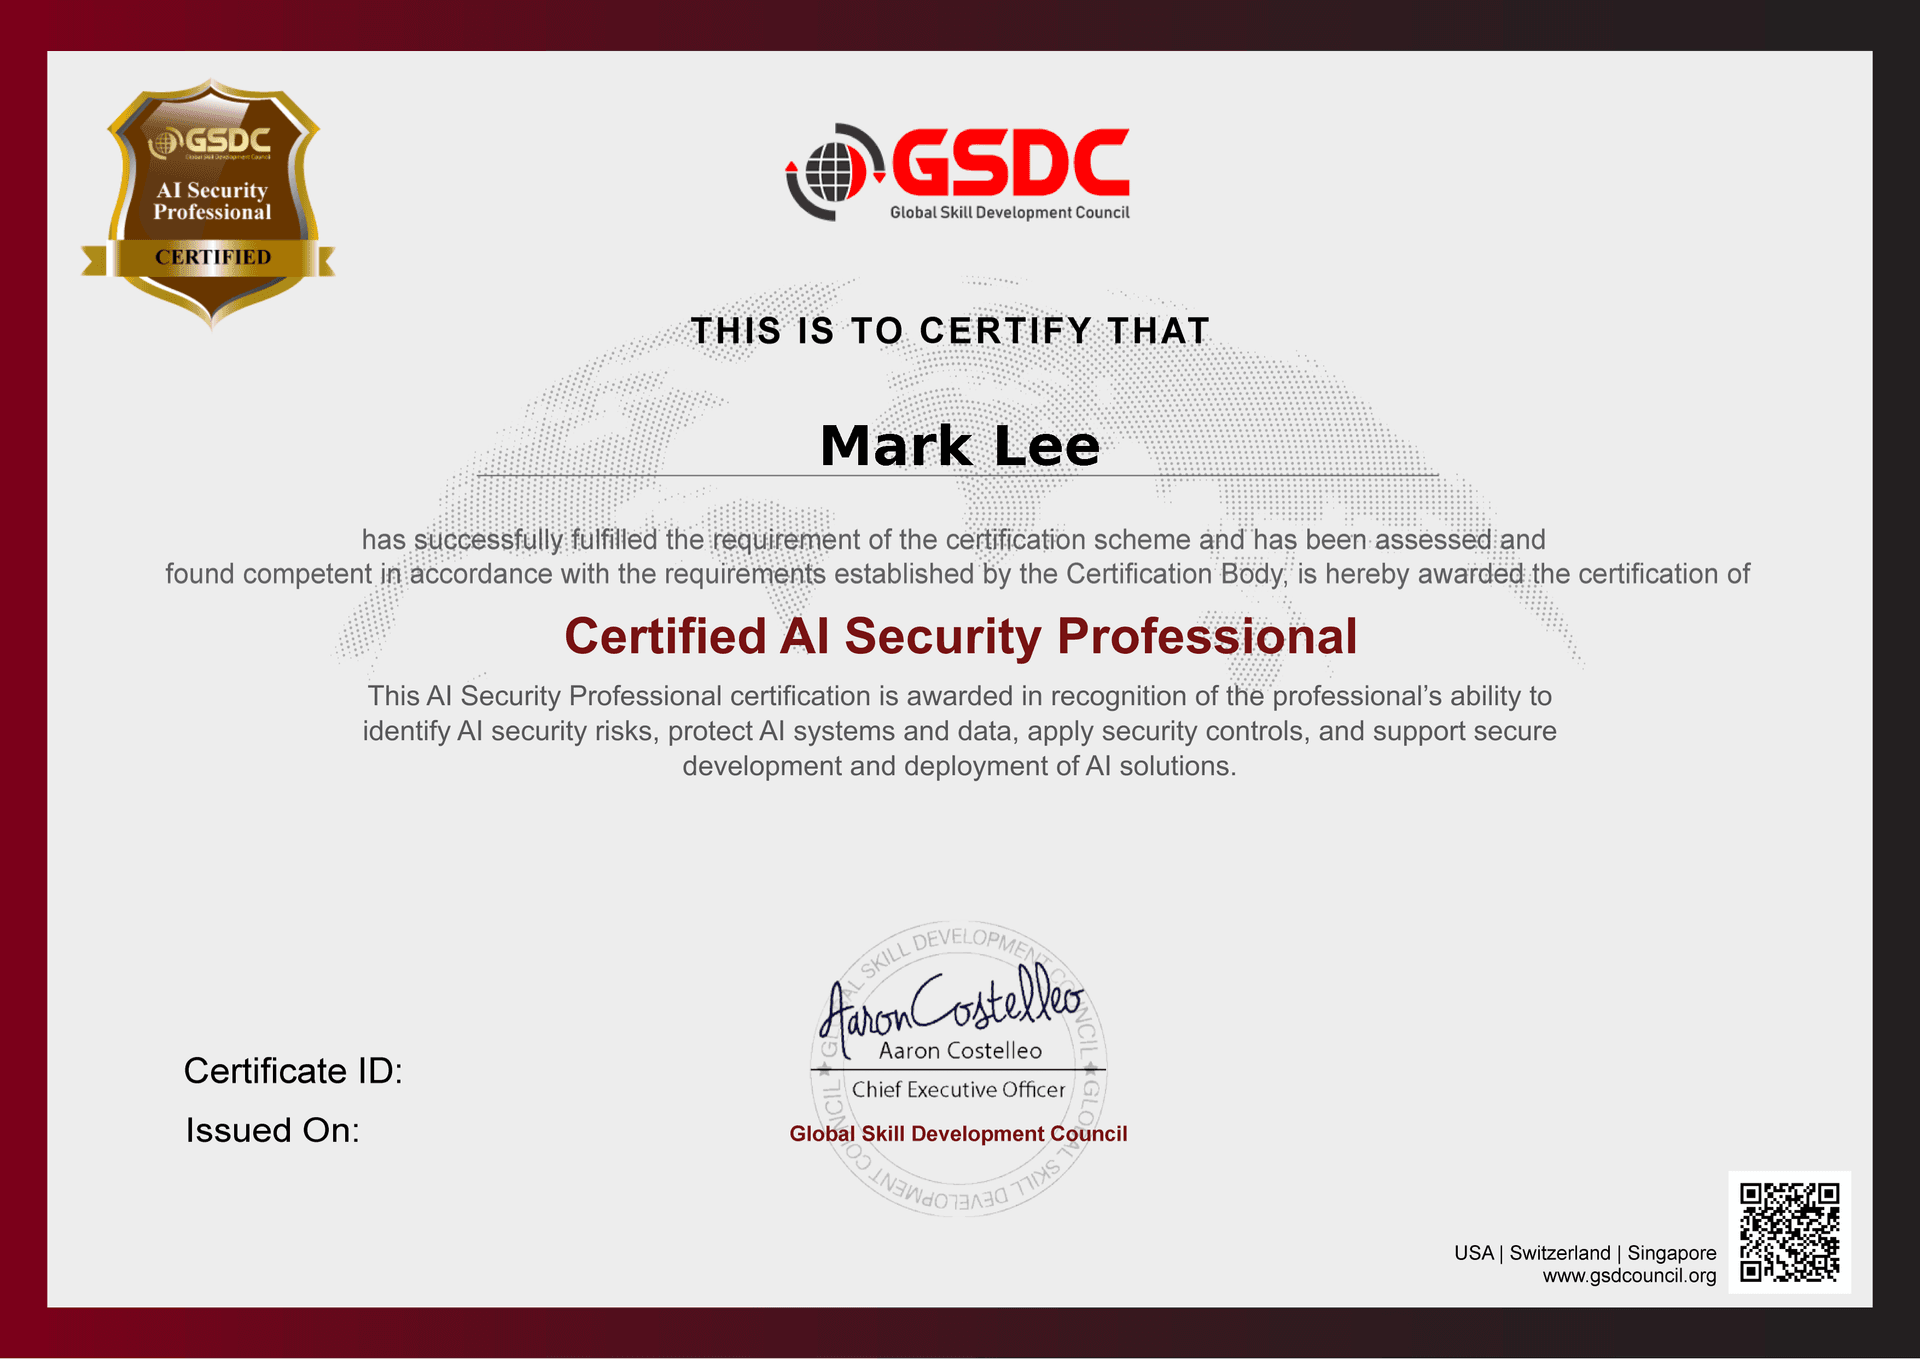
Number of Questions - 42
Exam Format - Multiple Choice
Language - English
Duration - 90 Minutes
Passing Score - 70%
Proctored - Yes
Certification Validity - 5 Years
Complimentary Retake - Yes